How to get the Certificate Common Name (FQDN) in the alerts description
Hello,
I am using the two script from Cole McDonald:
I've lightened the load slightly on the winCertCheck (which is technically no longer the same DS as I've replaced the entirety of the scripts with simplified .NET based powershell scripts to avoid using invoke-command which tends to lead to some resource constraint issues. This should help though, will keep the same instances alive from the old code as the output is identical to the previous version by @Jonathan Arnold:
<span style="color:#000000;">##--------------- Discovery ------------------##
$readOnly     = [System.Security.Cryptography.X509Certificates.OpenFlags]"ReadOnly"
$localMachine = [System.Security.Cryptography.X509Certificates.StoreLocation]"LocalMachine"
$store        = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\root", $localMachine )

$store.Open( $readOnly )

$store.Certificates `
| Select-Object {$_.Thumbprint + "##" + $_.Thumbprint + "##" + $_.Subject + $_.CommonName} `
| Format-Table -HideTableHeaders
##--------------------------------------------##</span>
<span style="color:#000000;">##-------------- Counters --------------------##
$readOnly     = [System.Security.Cryptography.X509Certificates.OpenFlags]"ReadOnly"
$localMachine = [System.Security.Cryptography.X509Certificates.StoreLocation]"LocalMachine"
$store        = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\root", $localMachine )

$store.Open( $readOnly )

$store.Certificates `
| Where-Object {($_.Thumbprint -like "##WILDVALUE##")} `
| Select-Object @{
	Name       = "DaysUntilExpire"
	Expression = {((Get-Date -Date $_.NotAfter) - (Get-Date)).Days}
} `
| Format-List
##--------------------------------------------##</span>(please note the line continuations to help readability of the code)
As always, neither I nor Beyond Impact warranty this code. It's working in our environment, I can't guarantee it'll work in yours. This doesn't account for anything that needs credentials other than what the collector uses.
==========================================================================================================================
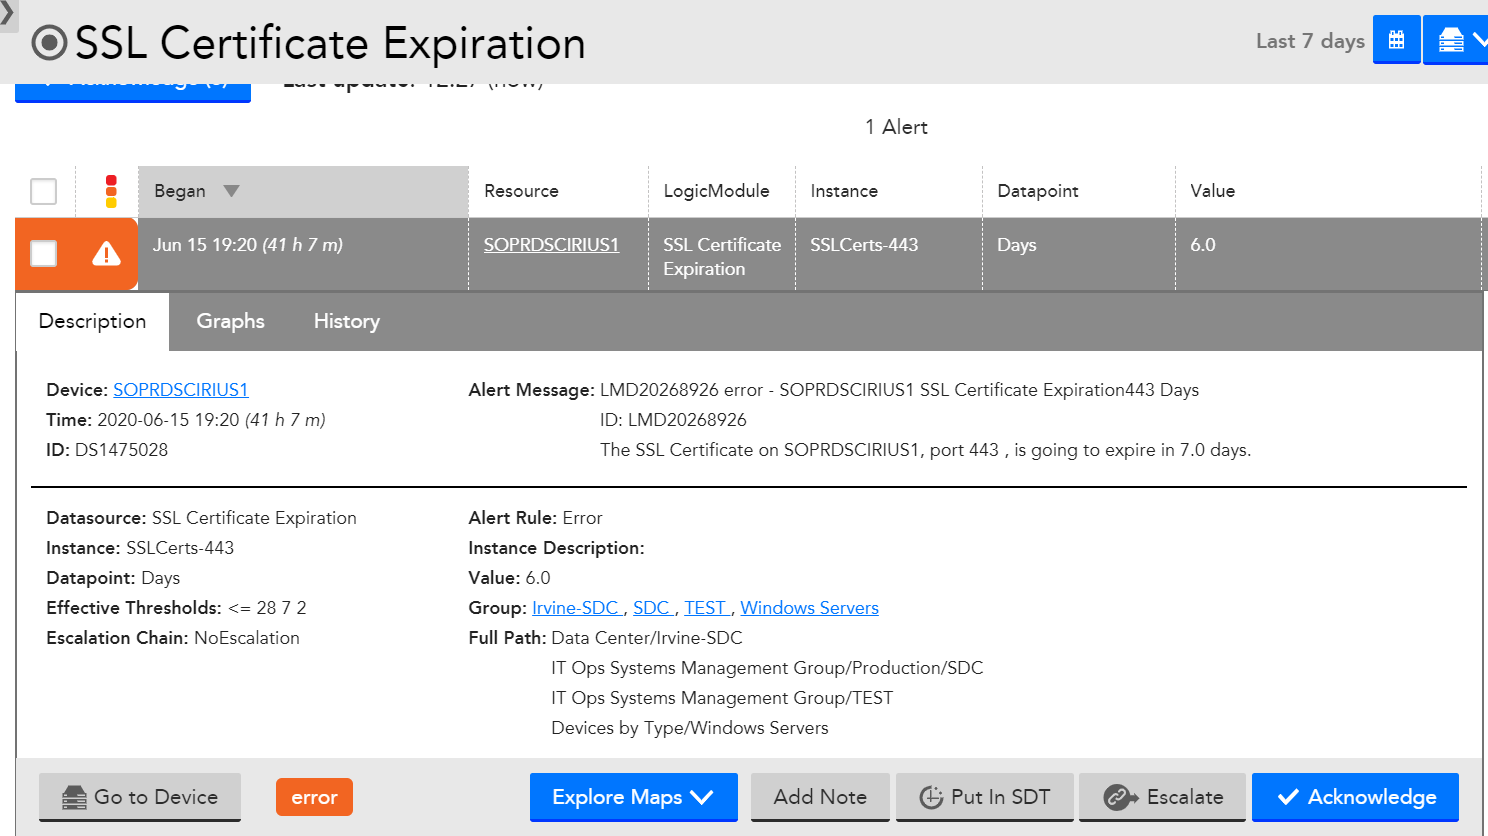
But when testing them on a current alert
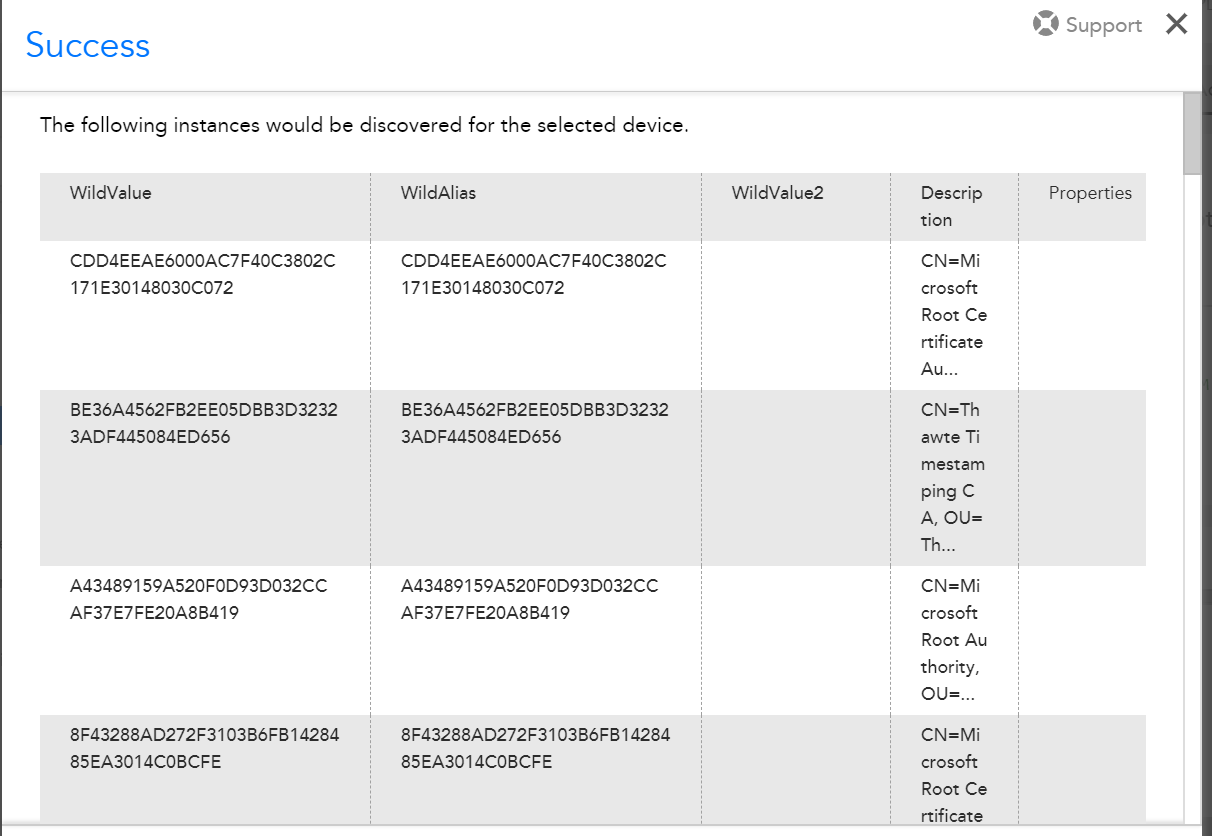
I could not get the correct common name displayed... and I do not see the certificate listed in the alert in the list of certificates produced by the script...
I might have missed something!!!
Thanks,
Dom

Dominique
OP5 years agoI see the Friendly Name in the info on the device:
SCCM SCUP Signing Certificate
Dominique
OP5 years agoHello Stuart,
Testing it now...
Thanks,
Dom
LM User
·5 years agoSure, if it's available. Where you do this bit in your discovery script:
You'd just need to output the friendly name in the "Select-Object" part. If the friendly name isn't available, you'll have to find out where the friendly name might be and script a way to fetch that.
The syntax of the output is:
ID##DisplayName##Description
So, if you want the friendly name as the display name, you'd change it to:
Assuming $_.FriendlyName contains the friendly name.
Dominique
OP5 years agoHello,
Is it possible to add the Friendly Name of the Certificate as well?
Thanks,
Dom
Vitor_Santos
·6 years agoCurrently, we have some clients that want to monitor several certificates on a box (example -> IIS server). Not only the server cert itself like 'SSLCerts-' does.
From this thread it seems this does the trick right? If yes, is it possible for you to share this DS?
Thank you!
LM User
·6 years agoI think you were running into some powershell width issues where it was only returning the first 120 characters of each line of output. I added the following to the beginning of both scripts to fix that:
I also modified your discovery script so that your WildAliases are unique. In one case, there was a certificate that didn't have a subject, so i added some logic to gracefully handle that. When the subject is known, the last 5 digits of the thumbprint are appended to the instance name to make it (hopefully) unique.
I also added some instance level properties for each instance. Cert.issuer, cert.serialnumber, and cert.thumbprint. These instances could be used to dynamically group certificates if wanted. If the instance level properties aren't needed, those lines can simply be commented out.
I also removed the valid range constraint just to make sure we were getting values on all of them. You had one certificate that was returning a negative number. If you want that negative number to open an alert, you can't exclude it from valid range. If you truly want to ignore negative values, just put the lower value in the valid range.
LM User
·6 years agoYou cannot put text into a datapoint. LM is giving you an error because you are trying to put text (the CN) into a number field (the datapoint).
Since your DS is in script mode and not batchscript mode, the only thing you need to output is the value itself.
I updated your collect script to contain just what it needs:
Also, your discovery has some problems that I started to resolve. Essentially, if the wildalias is the same, LM thinks it's the same instance. So, even though your WILDVALUE is distinct, the WILDALIAS on two of your certificates is not. Therefore, any certificates that have the same "$_.Subject" will be treated as the same instance.
Dominique
OP6 years agoAlso I noticed if I try to remove the Description or Property from the Collector Attributes Script the fields are again NaN with the error:
##-------------- Counters --------------------##
$readOnly = [System.Security.Cryptography.X509Certificates.OpenFlags]"ReadOnly"
$localMachine = [System.Security.Cryptography.X509Certificates.StoreLocation]"LocalMachine"
$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\my", $localMachine )
$properties = @(
@{n='WildValue';e={"##WildValue##"}},
@{n='CommonName';e={$_.Subject}},
@{n='Description';e={"##Description##"}},
@{n='Properties';e={"##Properties##"}},
@{n='DaysUntilExpire';e={($_.NotAfter -[datetime]::Today ).Days}}
)
$store.Open( $readOnly )
$store.Certificates `
| Where-Object {($_.Thumbprint -like "##WildValue##")} `
| Select-Object $properties
Also I could not get rid of the message in the CommonName even the field is filled ...? How to clean this error message?
Thanks,
Dom
Dominique
OP6 years agoAlmost there
CommonName is filled properly but there is still the error message !!! Why?
The Days to Expiration are correct
Dominique
OP6 years agoFinally the Test Script "Collector Attributes" is showing the correct value in the correct fields...
Trying to populate the Fields in the Datapoint now!!!
Dominique
OP6 years agoHello,
The field CommonName is filled up but not with the value expected, it has the WildValue F23456... and not the CN... From the script results I thought the WildAlias was filled with the CN (see attachment) but apparently it is not strange!!!...
The DaysToExpire is filled up in the Raw Request/Response but not but does not in the Datapoint. Not sure why the "##WildValue##.DaysToExpire" is not showing the value ...
I think the datapoints are not correctly defined...
Thanks,
Dom
Dominique
OP6 years agoHello,
Some updates:
======================================================================================================
##--------------- Discovery ------------------##
$readOnly = [System.Security.Cryptography.X509Certificates.OpenFlags]"ReadOnly"
$localMachine = [System.Security.Cryptography.X509Certificates.StoreLocation]"LocalMachine"
##$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\root", $localMachine )##
$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\my", $localMachine )
$store.Open( $readOnly )
$store.Certificates `
| Select-Object {$_.Thumbprint + "##" + $_.Subject } `
| Format-Table -HideTableHeaders
##--------------------------------------------##
======================================================================================================
and
======================================================================================================
##-------------- Counters --------------------##
$readOnly = [System.Security.Cryptography.X509Certificates.OpenFlags]"ReadOnly"
$localMachine = [System.Security.Cryptography.X509Certificates.StoreLocation]"LocalMachine"
$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\root", $localMachine )
$properties = @(
@{n='DaysUntilExpire';e={($_.NotAfter -[datetime]::Today ).Days}},
@{n='CommonName';e={"##WILDALIAS##"}}
)
$store.Open( $readOnly )
$store.Certificates `
| Where-Object {($_.Thumbprint -like "##WILDVALUE##")} `
| Select-Object $properties
======================================================================================================
with two datapoints ...
I am progressing but not yet okay... I did a poll and I have No data for CommonName and DaystoExpire but I have the information in the Raw Request/Response output so I think I have wrongly associated some fields!!!!
Thanks,
Dom
Dominique
OP6 years agoThanks for your patience Stuart...
I found the location
##$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\root", $localMachine )##
$store = new-object System.Security.Cryptography.X509Certificates.X509Store( "\\##SYSTEM.SYSNAME##\my", $localMachine )
Now I have the good certificate listed... I need to add as you said the expiration date set to combined both...
Thanks,
Dom
LM User
·6 years agoAh, i see. The problem is not that instance is getting discovered but the name isn't showing up, it's that the instance isn't getting discovered at all. Your script is not fetching those personal certs and will have to be modified somehow to pull in the personal certificates. Unfortunately, that's beyond my scripting skills as i'm not a windows/powershell guy. I could google it for you, but you probably don't need that kind of help from me.
Dominique
OP6 years agoHello,
I understand what I do on _SSL_Certificates does not affect the SSLCerts DS but I would like the CN to appear in the _SSLCertificates but it does not with this script... is it the location of the certificate which is worng?
I need the CN to appear in the Description of the Alert which is not the case for now. Apparently I see some certificates but not the one listed below with its CN value.. I have most of the certificates under "Trusted Root Certificates" but not the one under "Personal" folder...
It is the certificate listed below in the personal folder I need with its common name listed in clear text in its description...
Thanks,
Dom
LM User
·6 years agoYour collect script still isn't outputting anything and you don't have a threshold. There can't be any alerts where this would show up. What you're showing here is the alarm message from a completely different datasource.
Order of operations:
1. Get your collect script returning the number of days until expiration
2. Get your datapoint configured to read in the number of days into an actual datapoint
3. Set a threshold on the datapoint
4. Either build a custom alert message for that one datapoint (or modify the global alert template) to include the ##INSTANCE## token so that the instance's name is included in the email.
Either way, one datasource isn't going to add information to an alert from a different datasource. No matter what you do in _SSL_Certificates, it will not have any impact whatsoever on SSLCerts- alerts.
Dominique
OP6 years agoThanks Stuart, Yes on the certificate, or with the SSLCerts it appears in the subject line but it never shows up in the Alert ...
IT Ops Systems Management Group/Production/SDC
IT Ops Systems Management Group/TEST
Devices by Type/Windows Servers
Thanks,
Dom
LM User
·6 years agoIsn't the CN in the $_.Subject variable? It looks like it is. That would mean that the instance name is the CN.
You don't need the CN in a datapoint. The only datapoint you need is the "valid for". If you wanted to make more complex datapoints that compare the issued or expiration dates to now, you could do that, but it's not required for what it seems you need.
Dominique
OP6 years agoThanks Stuart but apparently I do not get the "common name" is it buried somewhere else than
$ !SSLCerts 10.32.156.78 443
Total received certs: 2
No.1 certificate
CN : CN=soprdscirius1.ad.xxxxxx.yyyy.zzz, OU=X Information Technology Services (MITS), O="Local, Los Angeles", STREET=757 Ww Plaza, L=Los Angeles, ST=CA, OID.2.5.4.17=90095, C=US
Issued At : Fri Jun 23 17:00:00 PDT 2017
Expire At : Tue Jun 23 16:59:59 PDT 2020
Valid for : 5 days
No.2 certificate
CN : CN=InCommon RSA Server CA, OU=InCommon, O=Internet2, L=Ann Arbor, ST=MI, C=US
Issued At : Sun Oct 05 17:00:00 PDT 2014
Expire At : Sat Oct 05 16:59:59 PDT 2024
Valid for : 1570 days
Thank,
Dom
LM User
·6 years agoAll of that makes sense and you are on the right track. The only thing i would add is that once you are getting the expiration date collecting successfully and the threshold set on the _SSL_Certificates DS, you might as well disable the SSLCerts- DS as you would be double alerting.
Dominique
OP6 years agoThanks Stuart,
The source of the question I am trying to resolve is coming from the datasource called "SSLCerts-" (displayname="SSL Certificate Expiration") which is incomplete and missing data (missing the "Common Name") for our team to be able to use it.
The DS "_SSL_Certificates" has been created to try to collect the information needed like the “common name”. I used this one as it seems simpler to use and update than “SSLCerts”, I might be wrong, let me know.
So the SSLCerts- DS is fine as is and for testing I didn’t want to touch it…. As it is already active in Production even if it is incomplete so far.
I am writing _SSL_Certificates as a replacement for SSLCerts- or as addition to it to provide more information
I will check for this error I did not see thanks for pointing it out the one causing the "No Data" error on collection.
The output is not enough for our technician as they need the common name to be able to renew the certificate this is a company requirement
I need the Common Name to be displayed as well as the Days before expiration both fields needs to there.
If it is possible to add the “Common Name” to the DS “SSLCerts-“ directly it is fine with me but I could not get it, it is why I went to the “_SSL_Certificates” which looks like will be able to display the “Common Name” and then I will adjust it to get the expiration date as well.
Thanks,
Dom
LM User
·6 years agoYeah, I think you're getting your DataSources crossed. The one from your screenshot is called "SSLCerts-" (displayname="SSL Certificate Expiration"). That DS is not a scripted DS, so the changes you are making to the scripted DS "_SSL_Certificates" will not impact the alerts opened by "SSLCerts-".
The SSLCerts- DS isn't meant to check all certs on a system, just those that are presented on a live web service discovered when the collector probes the TCP ports 443, 465, 636, and 5671.
Took a peek at your account and it looks like the current version of the script stores the CN as the WildAlias, which is perfectly fine (and probably preferable to what you were showing in your screenshot above). Let's talk about assumptions...
I assume that you are writing _SSL_Certificates as a replacement for SSLCerts-.
I assume that you can fix the script error that is currently causing the "No Data" error on collection.
Given those two assumptions, the output of your collection script should look something like this (actual values made up):
(Technically there are other simpler ways that you could output your data, but this way leaves the door open to adding more datapoints later on if desired.)
Your datapoint "CommonName" doesn't need to exist. Instead, you need to create a datapoint and the key would be "Days". You'd need to set a threshold on this datapoint so alarms open.
When an alert opens, you'd have the instance name in the alert, which is currently set to the CN.
Dominique
OP6 years agoHello,
I want to see the common name in the alert description but for now it is not displayed anywhere...
Thanks,
Dom
Dominique
OP6 years ago1. yes the alarm are coming from the SSL Certificate Expiration
2. No I did not see the common name anywhere in the current Datasource it is why I was creating a new one with the script in this thread.
LM User
·6 years agoAre the alarms in your first screenshot coming from the right DS? Looks like that alarm is coming from "SSL Certificate Expiration". Is that the same DS you built?
The common name is stored in the instance description right? If so, it should show up under the instance description in the alarm.